
Enterprise applications using Exchange Web Services (EWS)
AI summary
This policy detects app registrations using Exchange Web Services (EWS) permissions that Microsoft will deprecate in October 2026, helping you identify which apps need to migrate to Microsoft Graph API before the deadline. Use the linked resources to understand the migration timeline and identify all EWS dependencies in your tenant.
What it detects
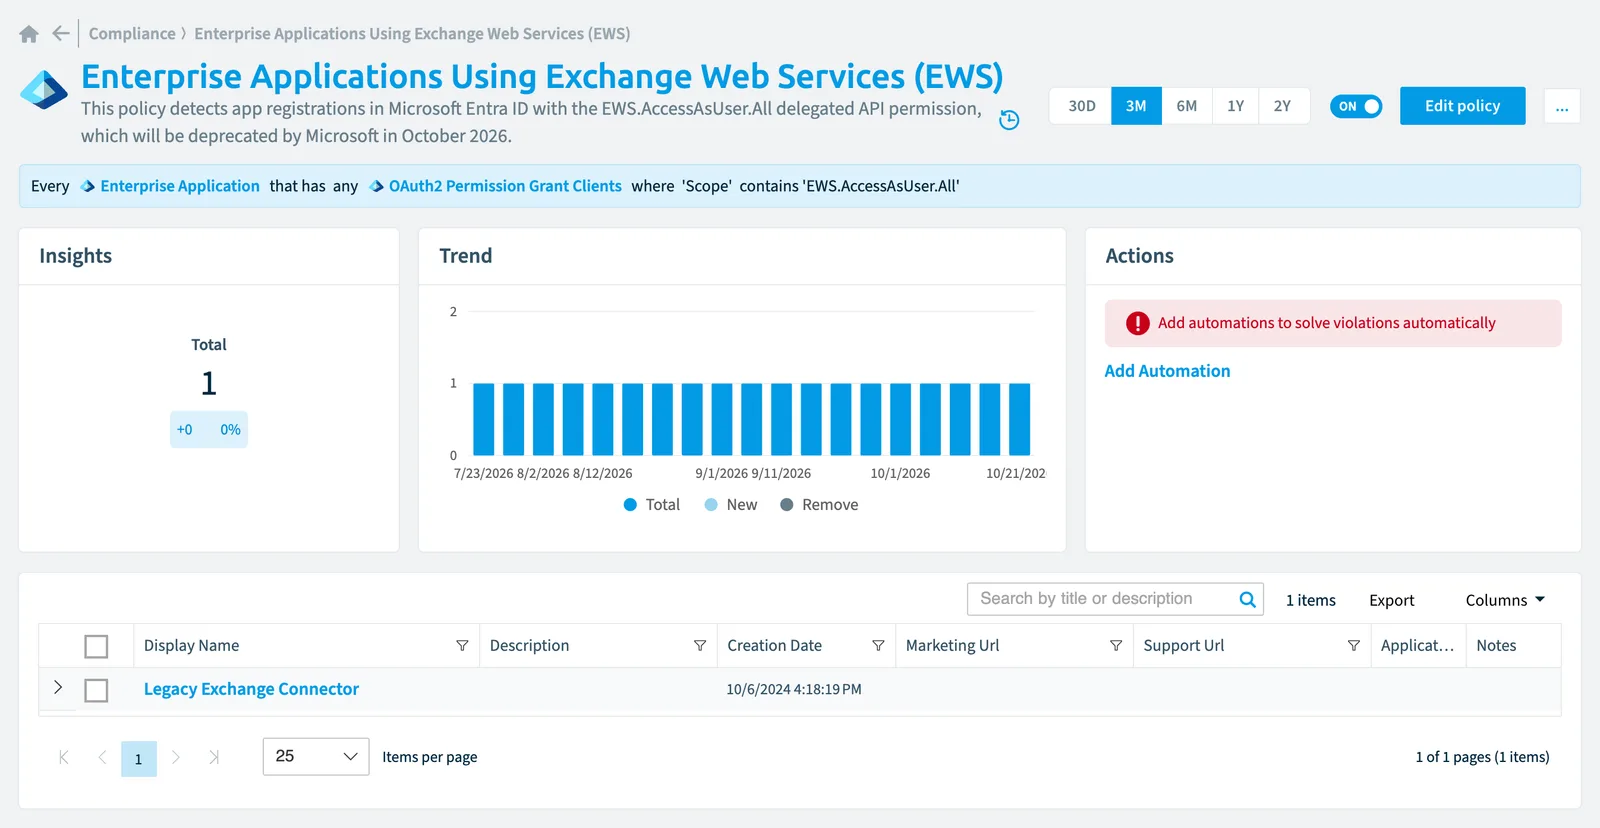
This policy detects app registrationsApp registrationAn app registration is the global definition of an application in Microsoft Entra ID.Read more in Microsoft Entra IDMicrosoft Entra IDMicrosoft Entra ID, formerly Azure Active Directory, is the Microsoft identity service behind every Microsoft 365 tenant.Read more with the EWS.AccessAsUser.All delegated API permission, which will be deprecated by Microsoft in October 2026.
Why it matters
Review each flagged app registration and work with the application owner to migrate from Exchange Web Services (EWS) to Microsoft Graph APIMicrosoft GraphMicrosoft Graph is the Microsoft API that gives access to the data of the Microsoft 365 services.Read more before October 2026. Use the EWS Deprecation Hub (https://aka.ms/ews1page50) to understand the timeline and the EWS Audit Tools (https://aka.ms/ewsTools) to identify all EWS dependencies across your tenant. For migration guidance, refer to the Microsoft Graph API documentation (https://learn.microsoft.com/en-us/graph/overview).
The rule
Every Enterprise Application that has any OAuth2 Permission Grant Clients where Scope contains 'EWS.AccessAsUser.All'
In Rencore Governance
Details
| Applies to | Enterprise application |
|---|---|
| Connector | Entra ID |
| Severity | High |
| Category | Security |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check Enterprise application objects:
- Enterprise applications that use SharePoint Online permissions (Information)
- Enterprise applications with full control or write permissions (Medium)
- Enterprise applications without owners (Medium)
- Enterprise applications (SharePoint add-ins) with certificates or client secrets (Medium)
- Enterprise applications that use Microsoft Graph permissions (Information)
- Enterprise applications (SharePoint add-ins) with expired certificates or client secrets (Medium)
Frequently asked questions
 What does the enterprise applications using Exchange Web Services (EWS) policy detect?
The Enterprise applications using Exchange Web Services (EWS) policy detects app registrations in Microsoft Entra ID with the EWS.AccessAsUser.All delegated API permission, which will be deprecated by Microsoft in October 2026.
Which objects does the enterprise applications using Exchange Web Services (EWS) policy check?
Which objects does the enterprise applications using Exchange Web Services (EWS) policy check?The Enterprise applications using Exchange Web Services (EWS) policy checks Enterprise application objects from the Entra ID inventory and reports each one that matches its rule as a violation.
How severe is a violation of the enterprise applications using Exchange Web Services (EWS) policy?
How severe is a violation of the enterprise applications using Exchange Web Services (EWS) policy?Violations of the Enterprise applications using Exchange Web Services (EWS) policy have High severity. The policy is in the Security category.
Which module includes the enterprise applications using Exchange Web Services (EWS) policy?
Which module includes the enterprise applications using Exchange Web Services (EWS) policy?The Enterprise applications using Exchange Web Services (EWS) policy comes with the Entra ID connector in the Digital Workplace module of Rencore Governance, which every Plan includes.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?