
Applications with client secrets that are about to expire
AI summary
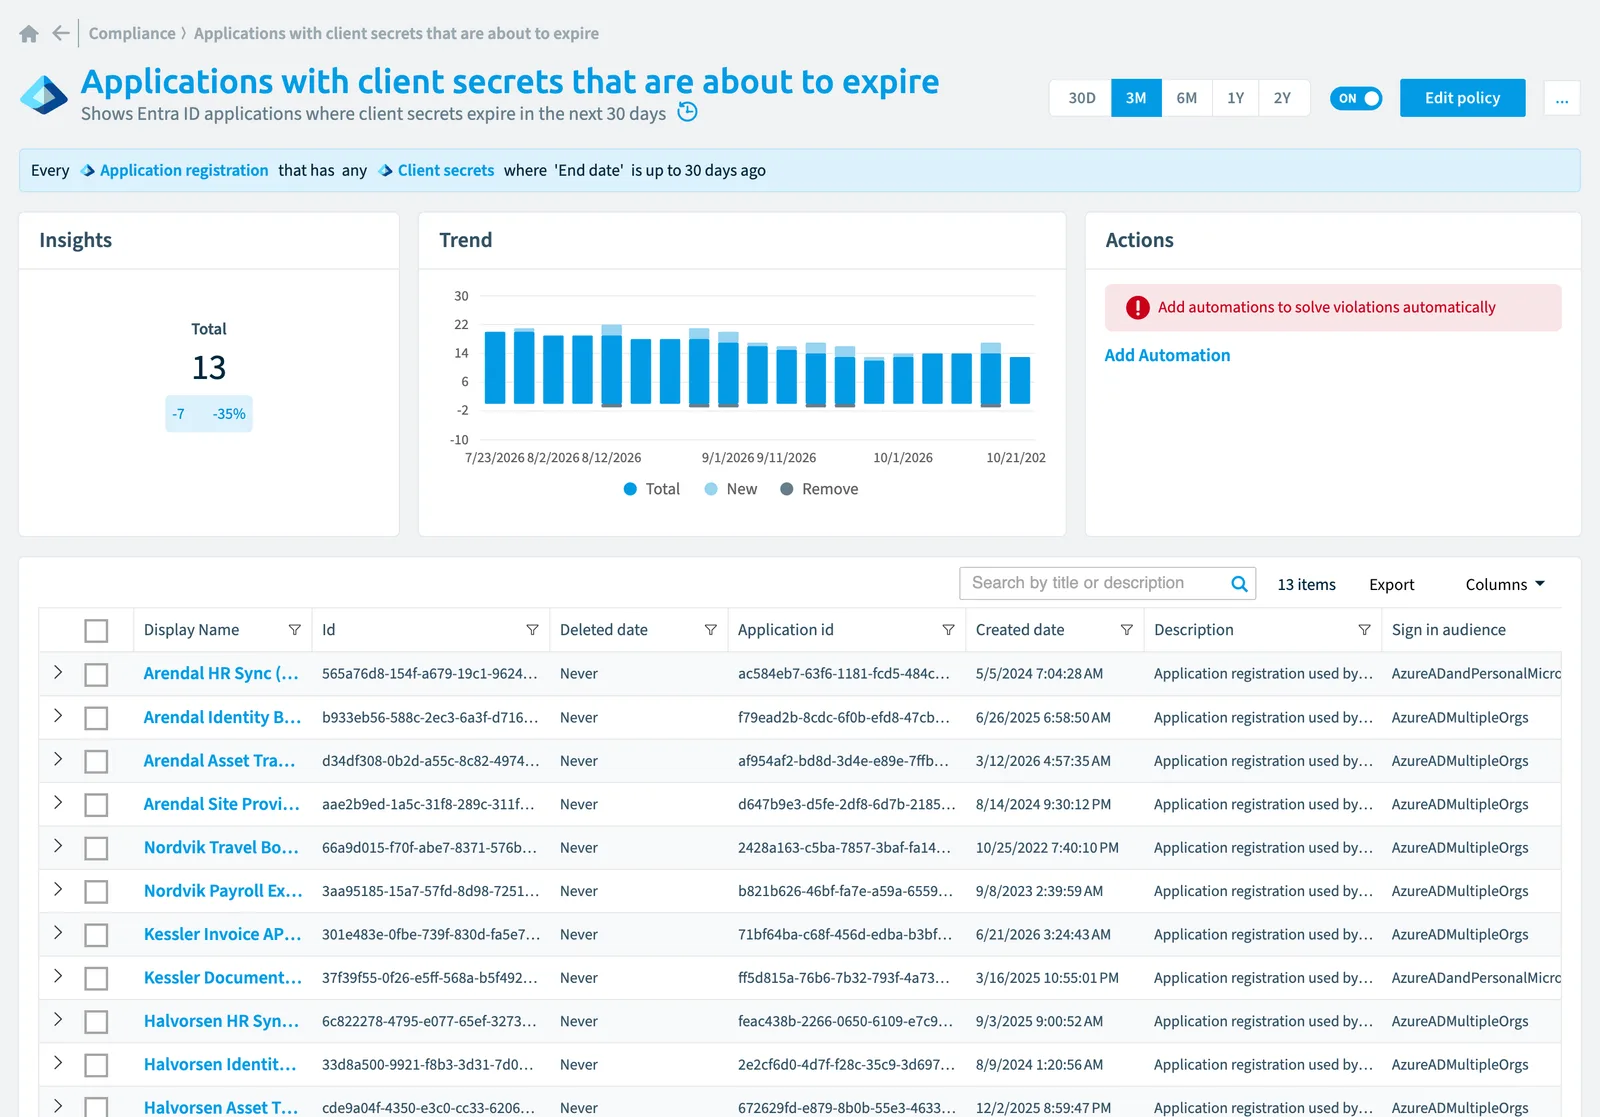
Rencore identifies Entra ID applications with client secrets expiring within the next 30 days. When secrets expire, applications cannot sign in to Microsoft Entra ID and their dependent integrations stop working, so you need to renew them beforehand.
What it detects
Shows Entra IDMicrosoft Entra IDMicrosoft Entra ID, formerly Azure Active Directory, is the Microsoft identity service behind every Microsoft 365 tenant.Read more applications where client secretsClient secretA client secret is a password-like string that an app registration uses to prove its identity when it requests a token from Microsoft Entra ID.Read more expire in the next 30 days.
Why it matters
When a client secret expires, the application can no longer sign in to Microsoft Entra ID, and the integrations, scheduled jobs and connectors that depend on it stop working. Secrets created in the Microsoft Entra admin centerAdmin centerAn admin center is the web portal where administrators manage one Microsoft service, such as the Microsoft 365 admin center, the Teams admin center or the Microsoft Entra admin center.Read more last at most 24 months, so every app with a secret needs a renewal on a known date. Tell the application owner now, add a new secret, update the app's configuration and then delete the old secret.
The rule
Every Application registration that has any Client secrets where End date is up to 30 days ago
In Rencore Governance
Details
| Applies to | Application registration |
|---|---|
| Connector | Entra ID |
| Severity | High |
| Category | Operation |
| Recommended | No |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check Application registration objects:
Frequently asked questions
What does the applications with client secrets that are about to expire policy detect?
The Applications with client secrets that are about to expire policy shows Entra ID applications where client secrets expire in the next 30 days.
Which objects does the applications with client secrets that are about to expire policy check?
The Applications with client secrets that are about to expire policy checks Application registration objects from the Entra ID inventory and reports each one that matches its rule as a violation.
How severe is a violation of the applications with client secrets that are about to expire policy?
Violations of the Applications with client secrets that are about to expire policy have High severity. The policy is in the Operation category.
Which module includes the applications with client secrets that are about to expire policy?
The Applications with client secrets that are about to expire policy comes with the Entra ID connector in the Digital Workplace module of Rencore Governance, which every Plan includes.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?