
Unauthenticated public agent security risk
AI summary
Rencore Governance flags Copilot Agents published without authentication as a high-severity security risk. Implement authentication methods, restrict access, and audit conversations to prevent malicious actors from extracting sensitive information or manipulating agent behavior.
What it detects
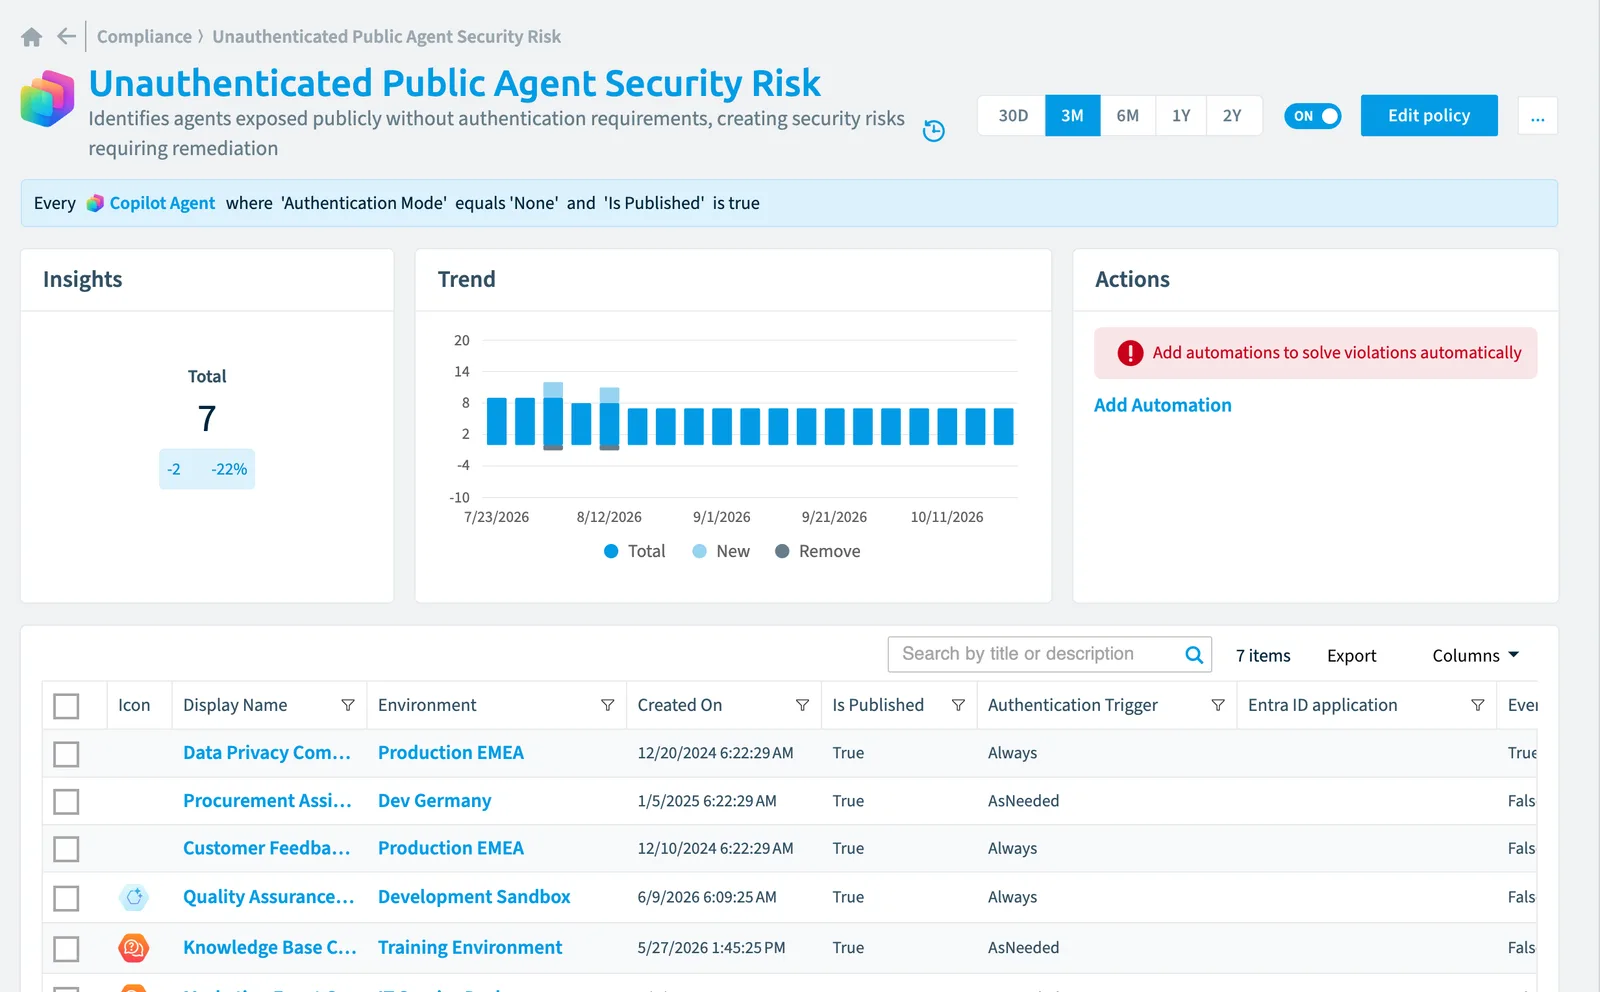
Identifies agents exposed publicly without authentication requirements, creating security risks requiring remediation.
Why it matters
Secure publicly exposed agents by implementing authentication requirements immediately, as unauthenticated access creates vulnerabilities that could allow malicious actors to extract sensitive information, manipulate agent behavior, or generate unauthorized costs. Configure appropriate authentication methods, restrict access, and audit existing conversations to ensure no sensitive data has been exposed.
The rule
Every Copilot Agent where Authentication Mode equals 'None' and Is Published is true
In Rencore Governance
Details
| Applies to | Copilot agent |
|---|---|
| Connector | Copilot Studio |
| Severity | High |
| Category | Security |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check Copilot agent objects:
- Resource Groups with too many services (High)
- Autonomous Copilot agent risk (Medium)
- Autonomous Copilot agent with scheduled trigger (High)
- External web content dependency risk (Medium)
- Orphaned Copilot agent ownership gap (Medium)
- Stale unpublished Copilot agents - 30 days (Medium)
- Unused agent cleanup candidate - 90 days (Medium)
Frequently asked questions
What does the unauthenticated public agent security risk policy detect?
The Unauthenticated public agent security risk policy identifies agents exposed publicly without authentication requirements, creating security risks requiring remediation.
Which objects does the unauthenticated public agent security risk policy check?
The Unauthenticated public agent security risk policy checks Copilot agent objects from the Copilot Studio inventory and reports each one that matches its rule as a violation.
How severe is a violation of the unauthenticated public agent security risk policy?
Violations of the Unauthenticated public agent security risk policy have High severity. The policy is in the Security category.
Which module includes the unauthenticated public agent security risk policy?
The Unauthenticated public agent security risk policy comes with the Copilot Studio connector in the AI & Agents module of Rencore Governance, an add-on module on the Premium and Enterprise Plans.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?