Connector used with a personal login
AI summary
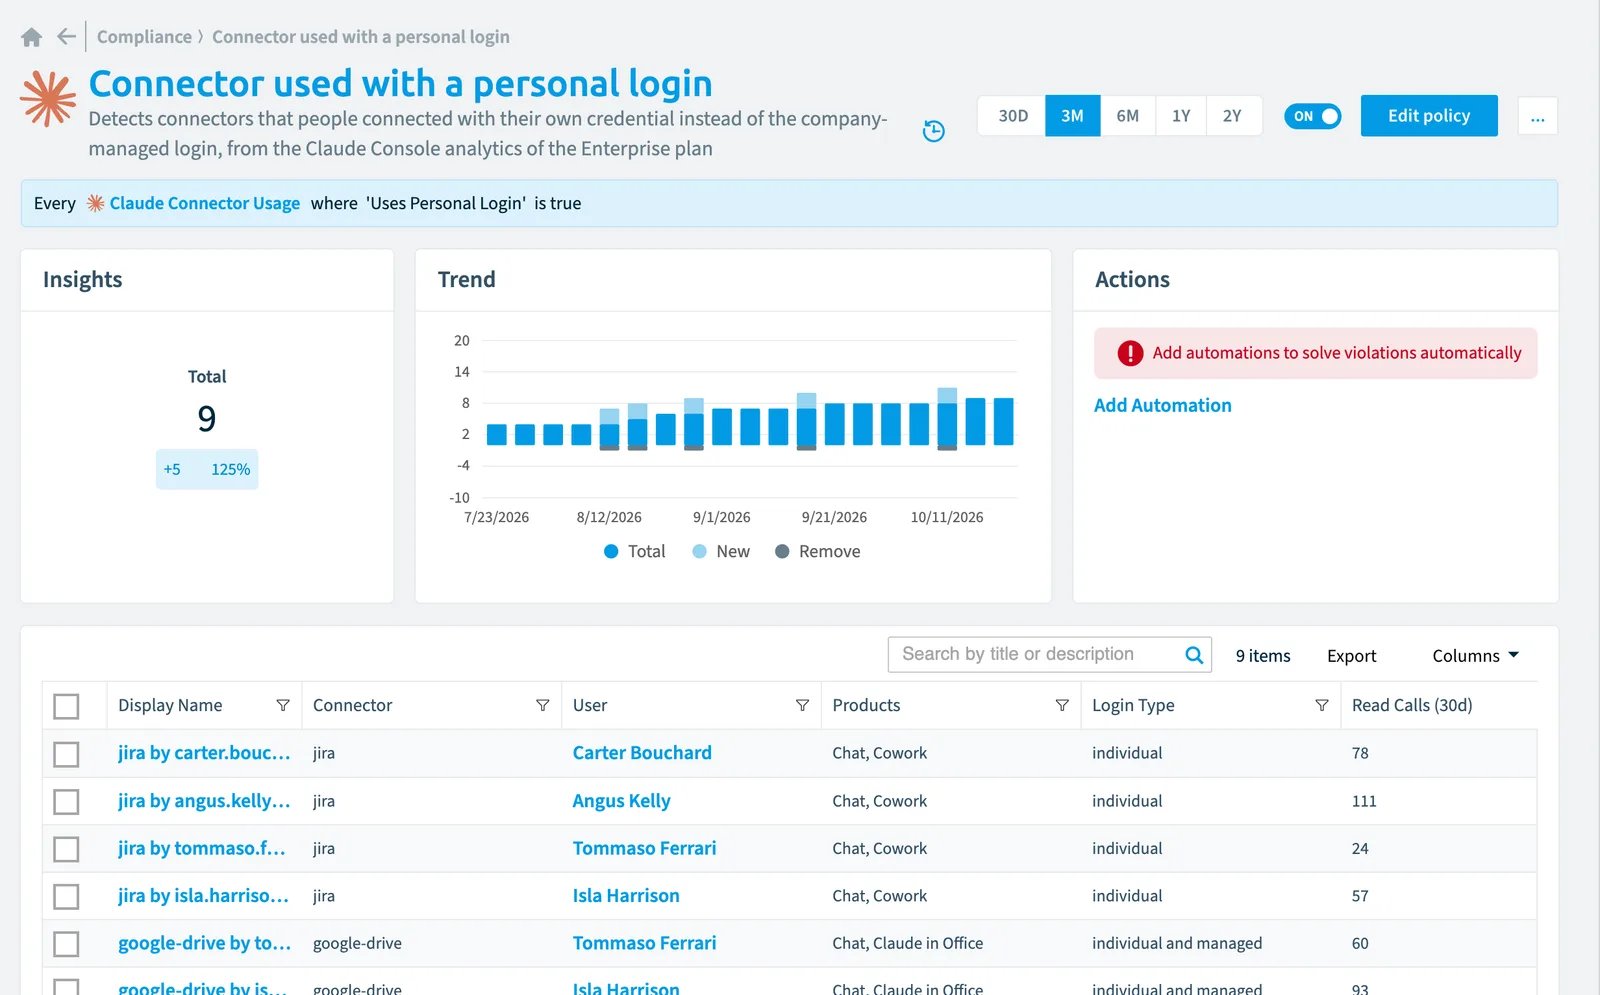
Rencore detects Claude connectors that people connected with their own login instead of a company-managed credential. Since they operate outside your organization's control and survive offboarding, move these connectors to managed credentials or remove them.
What it detects
Detects connectors that people connected with their own credential instead of the company-managed login, from the Claude Console analytics of the Enterprise planPlanA Plan is the edition of Rencore Governance in your Subscription: Professional, Premium or Enterprise.Read more.
Why it matters
A connector the user connected with their own credential runs on a personal account outside the control of the organization: it survives offboarding, it is invisible to the identity provider, and whatever it reads or writes passes through an identity nobody administers. Enterprise Managed Auth provisions the credential centrally instead. Review every connector reported with a personal login and either move it to a managed credential or remove the connector. Anthropic reports the login type from 1 July 2026 onward, so earlier windows carry no value at all - which is not the same as a managed login.
The rule
Every Claude Connector Usage where Uses Personal Login is true
In Rencore Governance
Details
| Applies to | Claude connector usage |
|---|---|
| Connector | Claude Enterprise |
| Severity | Medium |
| Category | Security |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check Claude connector usage objects:
- Connector performs write actions (Medium)
Frequently asked questions
What does the connector used with a personal login policy detect?
The Connector used with a personal login policy detects connectors that people connected with their own credential instead of the company-managed login, from the Claude Console analytics of the Enterprise plan.
Which objects does the connector used with a personal login policy check?
The Connector used with a personal login policy checks Claude connector usage objects from the Claude Enterprise inventory and reports each one that matches its rule as a violation.
How severe is a violation of the connector used with a personal login policy?
Violations of the Connector used with a personal login policy have Medium severity. The policy is in the Security category.
Which module includes the connector used with a personal login policy?
The Connector used with a personal login policy comes with the Claude Enterprise connector (in preview) in the AI & Agents module of Rencore Governance, an add-on module on the Premium and Enterprise Plans.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?