
Device
AI summary
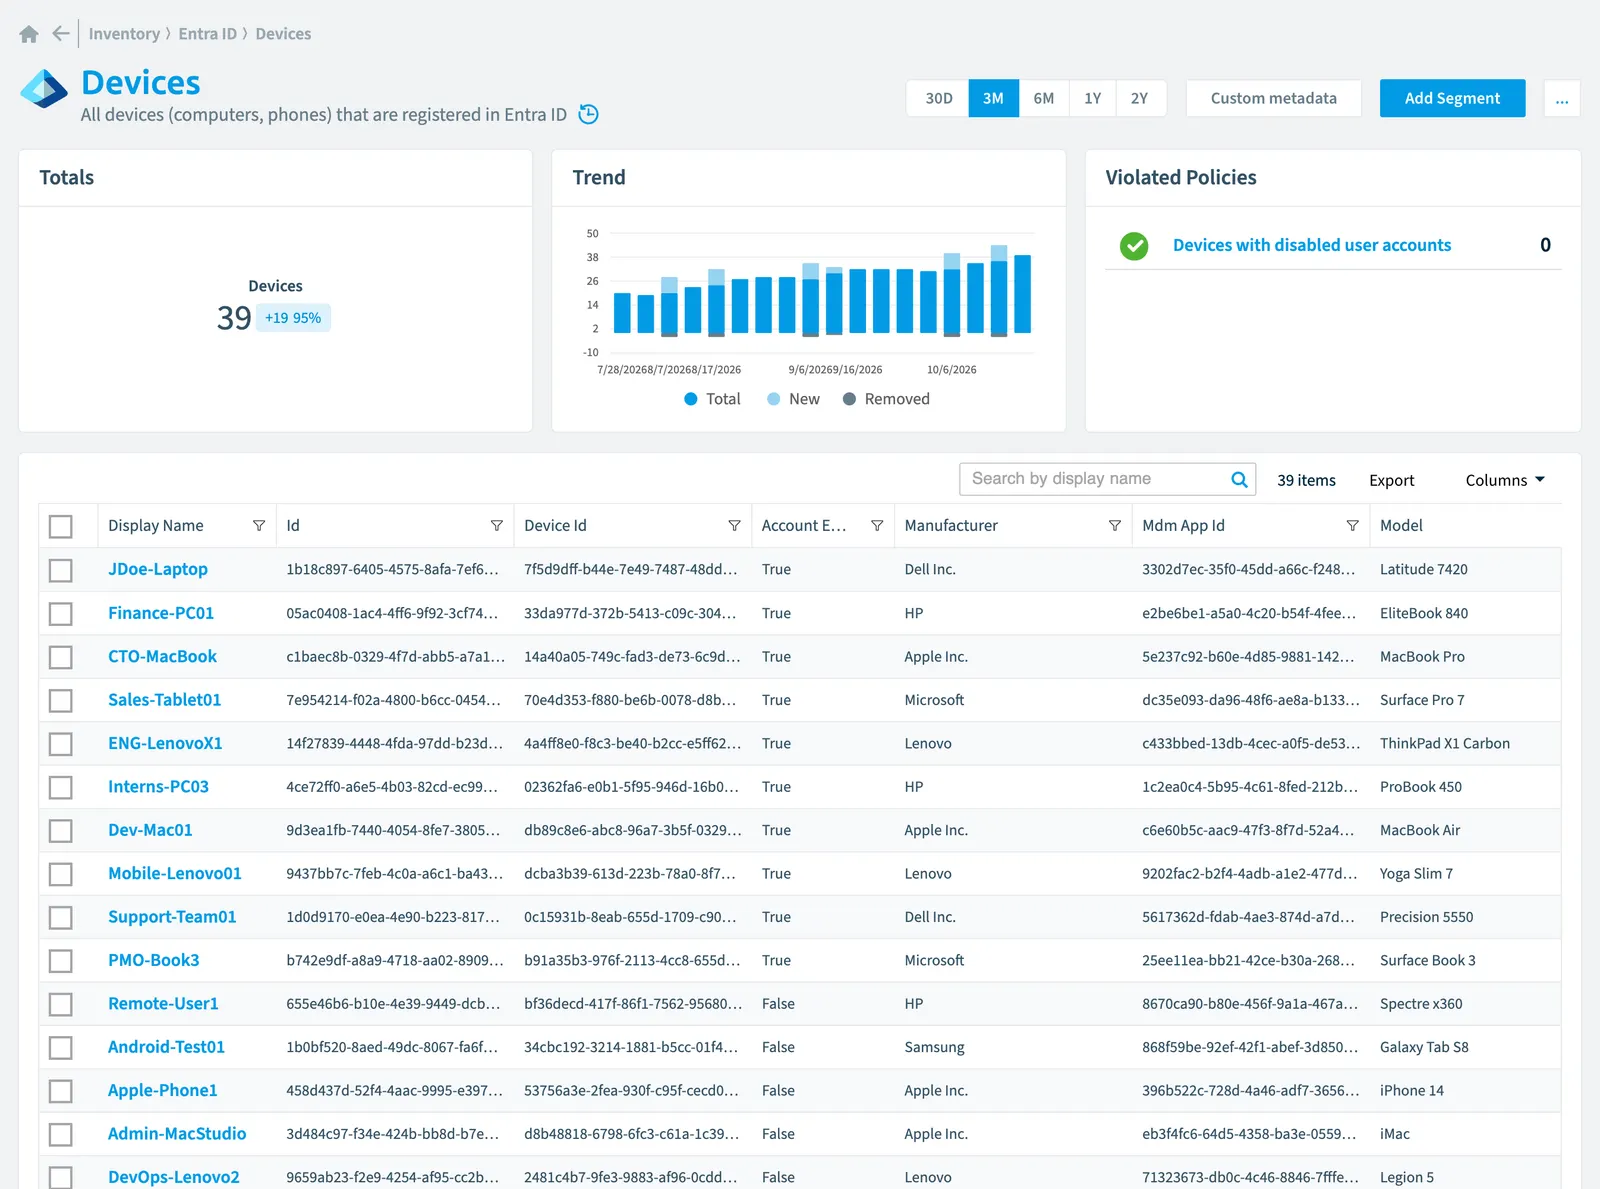
Device objects represent all computers and phones registered in Entra ID within Rencore Governance. Each device includes 25 properties organized across 9 groups covering identity, activity, security status, and management settings. Rencore scans devices on a configurable schedule (daily by default) and uses device properties in policies to check compliance.
All devices (computers, phones) that are registered in Entra IDMicrosoft Entra IDMicrosoft Entra ID, formerly Azure Active Directory, is the Microsoft identity service behind every Microsoft 365 tenant.Read more
Part of the Entra ID inventory.
In Rencore Governance
Scan settings
| Default scanning interval | Allowed scanning intervals | Data removal during incremental scan |
|---|---|---|
| Daily | Daily, Weekly, Bi-Weekly, Monthly, Never, Initial | Yes |
Properties
25 properties in 9 groups. Open a group to see its properties.
Name and identity 8
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Id | String | The unique identifier for the device. | {{Device. |
| Device Id | String | Unique identifier set by Azure Device Registration Service at the time of registration. | {{Device. |
| Device Version | Int32 | For internal use only. | {{Device. |
| Display Name | String | {{Device. | |
| Mdm App Id | String | Application identifier used to register device into MDM. | {{Device. |
| Operating System Version | String | The version of the operating system on the device. | {{Device. |
| Profile Type | String | The profile type of the device. Possible values: RegisteredDevice (default), SecureVM, Printer, Shared, IoT. Allowed values: IoT, Printer, RegisteredDevice, SecureVM, Shared. | {{Device. |
| Trust Type | String | Type of trust for the joined device. Possible values: Workplace (indicates bring your own personal devices), AzureAd (Cloud only joined devices), EntraID (on-premises domain joined devices joined to Entra ID). Allowed values: EntraID, ServerAd, Workplace. | {{Device. |
Activity and usage 3
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Approximate Last Sign In Date | DateTime | The timestamp type represents date and time information using ISO 8601 format and is always in UTC time. For example, midnight UTC on Jan 1, 2014 is 2014-01-01T00:00:00Z. | {{Device. |
| Last scan update | DateTime | Shows when this object was last updated in a scan. If an object is found during a scan but no property has been changed this date will not change. | {{Device. |
| On Premises Last Sync Date | DateTime | The last time at which the object was synced with the on-premises directory. The Timestamp type represents date and time information using ISO 8601 format and is always in UTC time. For example, midnight UTC on Jan 1, 2014 is 2014-01-01T00:00:00Z. | {{Device. |
AI and agents 1
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Model | String | Model of the device. | {{Device. |
Dates and scanning 1
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Initially Scanned | DateTime | Shows when this object was initially found in a scan. | {{Device. |
Sharing and access 1
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Device Ownership | String | Ownership of the device. This property is set by Intune. Possible values are: unknown, company, personal. Allowed values: Company, Personal, Unknown. | {{Device. |
Security and compliance 6
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Account Enabled | Boolean | true if the account is enabled; otherwise, false. | {{Device. |
| Compliance Expiration Date | DateTime | The timestamp when the device is no longer deemed compliant. The timestamp type represents date and time information using ISO 8601 format and is always in UTC time. For example, midnight UTC on Jan 1, 2014 is 2014-01-01T00:00:00Z. | {{Device. |
| On Premises Sync Enabled | Boolean | true if this object is synced from an on-premises directory; false if this object was originally synced from an on-premises directory but is no longer synced; null if this object has never been synced from an on-premises directory (default). | {{Device. |
| Risk Score | Int32 | Stores risk score | {{Device. |
| Risk Score Update | DateTime | Stores risk score update | {{Device. |
| Risk Score Value | String | Stores risk score value like Low_Low | {{Device. |
Settings 2
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Is Compliant | Boolean | true if the device complies with Mobile Device Management (MDM) policies; otherwise, false. This can only be updated by Intune for any device OS type or by an approved MDM app for Windows OS devices. | {{Device. |
| Is Managed | Boolean | true if the device is managed by a Mobile Device Management (MDM) app; otherwise, false. This can only be updated by Intune for any device OS type or by an approved MDM app for Windows OS devices. | {{Device. |
Custom attributes 1
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Device Metadata | String | For internal use only. | {{Device. |
Other properties 2
| Property | Type | Description | Automation placeholder |
|---|---|---|---|
| Manufacturer | String | Manufacturer of the device. | {{Device. |
| Operating System | String | The type of operating system on the device. | {{Device. |
Relations
| Relation | Connector | Description |
|---|---|---|
| User | Microsoft 365Microsoft 365Microsoft 365 is the Microsoft cloud suite of Teams, SharePoint, OneDrive, Exchange and the Office apps.Read more | User who ownes the device |
| User | Microsoft 365 | User who uses the device |
Segments
This object does currently not have any segments.
Actions
This object does currently not have any actions.
Policies that check this object
| Policy | Severity | Description |
|---|---|---|
| Devices with disabled user accounts | Medium | Shows devices with disabled owners or user accounts |
Frequently asked questions
What is the device object in Rencore Governance?
All devices (computers, phones) that are registered in Entra ID. Device is an object type in the Entra ID inventory of Rencore Governance.
Which properties does Rencore Governance collect for device?
Rencore Governance collects 25 properties for Device, such as Account Enabled, Approximate Last Sign In Date, Compliance Expiration Date and 22 more.
Which policies check device objects?
1 built-in policy checks Device objects, such as Devices with disabled user accounts.
How often is device scanned?
By default daily. You can change the scan interval of Device objects under Configure objects (daily, weekly, bi-weekly, monthly, never or initial (collected once)). The interval is a target, not a guarantee: a scan can run later than planned.
Which module includes the Entra ID connector?
Which module includes the Entra ID connector?The Entra ID connector is part of the Digital Workplace module of Rencore Governance, which every Plan includes. The connector is generally available.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?