
Groups with disabled user accounts

AI summary
Disabled accounts in groups create security vulnerabilities and may receive sensitive communications. Use a Rencore Governance policy to automatically remove disabled accounts and reassign group ownership to active users.
What it detects
Shows groups with users (owners and members) that have disabled accounts.
Why it matters
Disabled accounts retaining group membership create security vulnerabilities, may receive sensitive communications, and complicate access management across your organization. Use Rencore Governance to identify and automatically remove disabled accounts from all groups while reassigning ownership responsibilities to active users, ensuring continuous group management and preventing orphaned resources that could impact collaboration and security.
The rule
Every Group that has any Group Members where Account Enabled is false
In Rencore Governance
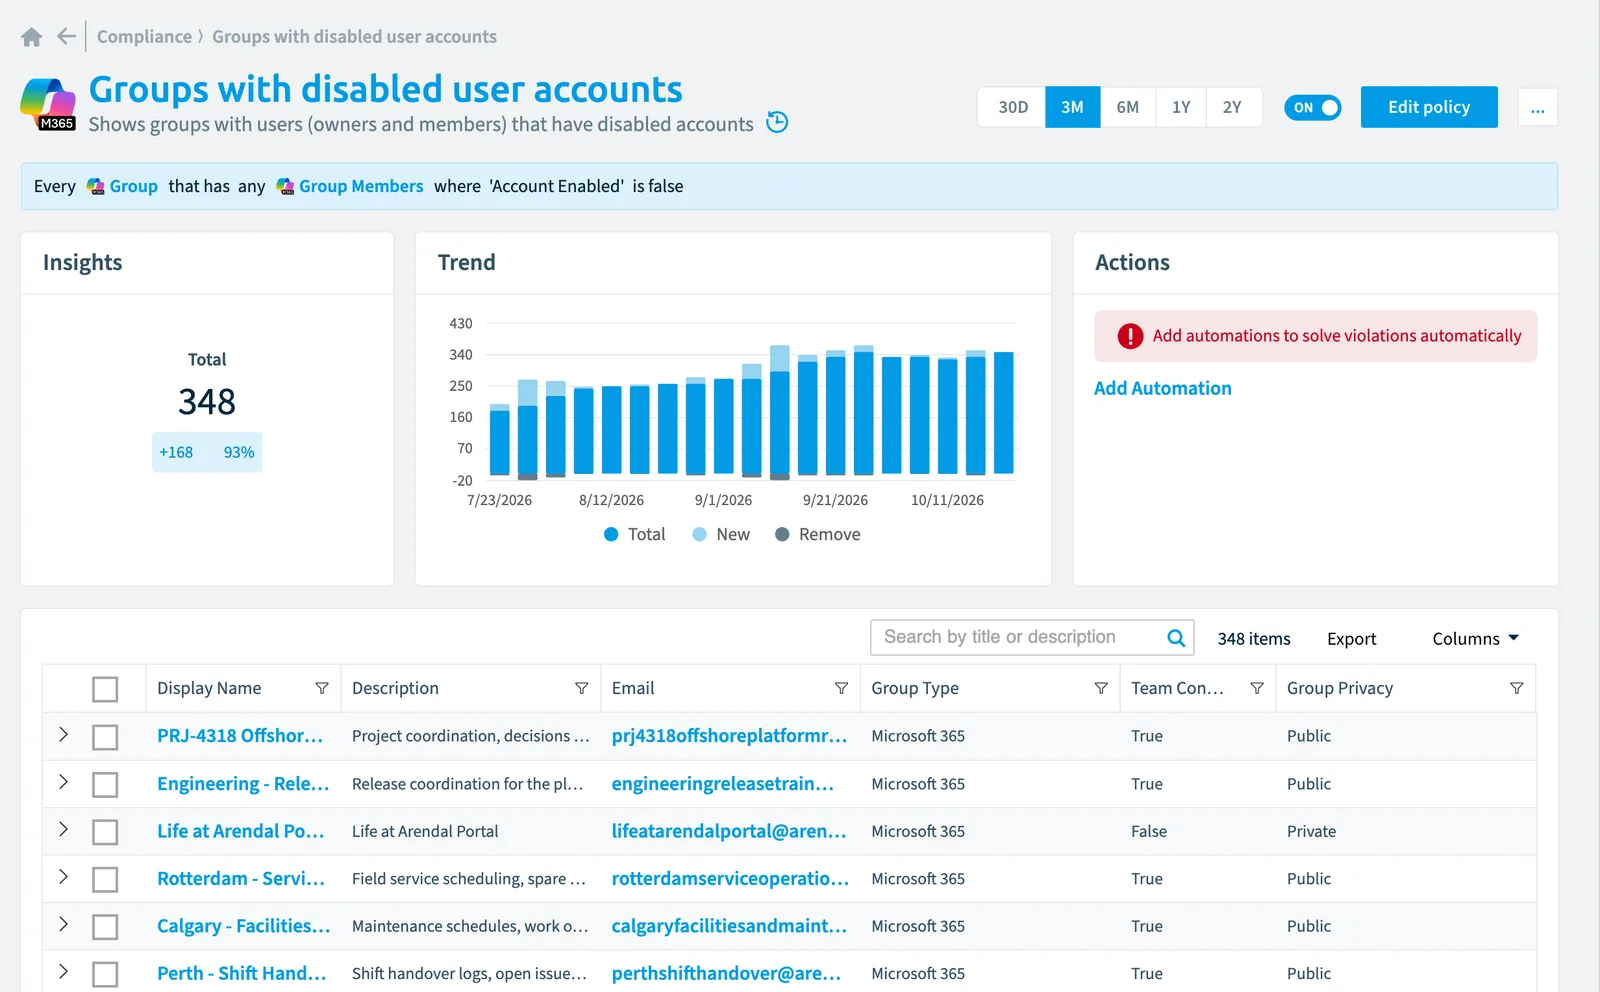
Details
| Applies to | Group |
|---|---|
| Connector | Microsoft 365 |
| Severity | Medium |
| Category | User OffboardingLeaverA leaver is someone who has left your organization but whose account may still hold licenses, workspaces, ownership and OneDrive content.Read more |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check Group objects:
- Groups with external users (Medium)
- Groups with external owners (High)
- Groups with very few owners (Medium)
Frequently asked questions
What does the groups with disabled user accounts policy detect?
The Groups with disabled user accounts policy shows groups with users (owners and members) that have disabled accounts.
Which objects does the groups with disabled user accounts policy check?
The Groups with disabled user accounts policy checks Group objects from the Microsoft 365 inventory and reports each one that matches its rule as a violation.
How severe is a violation of the groups with disabled user accounts policy?
Violations of the Groups with disabled user accounts policy have Medium severity. The policy is in the User Offboarding category.
Which module includes the groups with disabled user accounts policy?
The Groups with disabled user accounts policy comes with the Microsoft 365 connector in the Digital Workplace module of Rencore Governance, which every Plan includes.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?