
Inactive internal users

AI summary
Rencore Governance detects internal users who have not signed in for more than six months, who may represent terminated employees or extended leaves. These inactive accounts create security risks and consume resources; you should review them regularly and disable those no longer needed while following data retention policies.
What it detects
Shows internal users that have not signed in for more than 6 month.
Why it matters
Internal users inactive for six months may represent terminated employees, extended leaves, or role changes, but their active accounts pose security risks and consume resources. Review inactive internal accounts to determine current status, disable accounts no longer needed while following proper data retention policies, and implement automated detection through Rencore Governance to ensure timely account lifecycle management and reduced security exposure.
The rule
Every User where Last Sign-In is more than 6 months ago and Last Sign-In is not default and Is External is false
In Rencore Governance
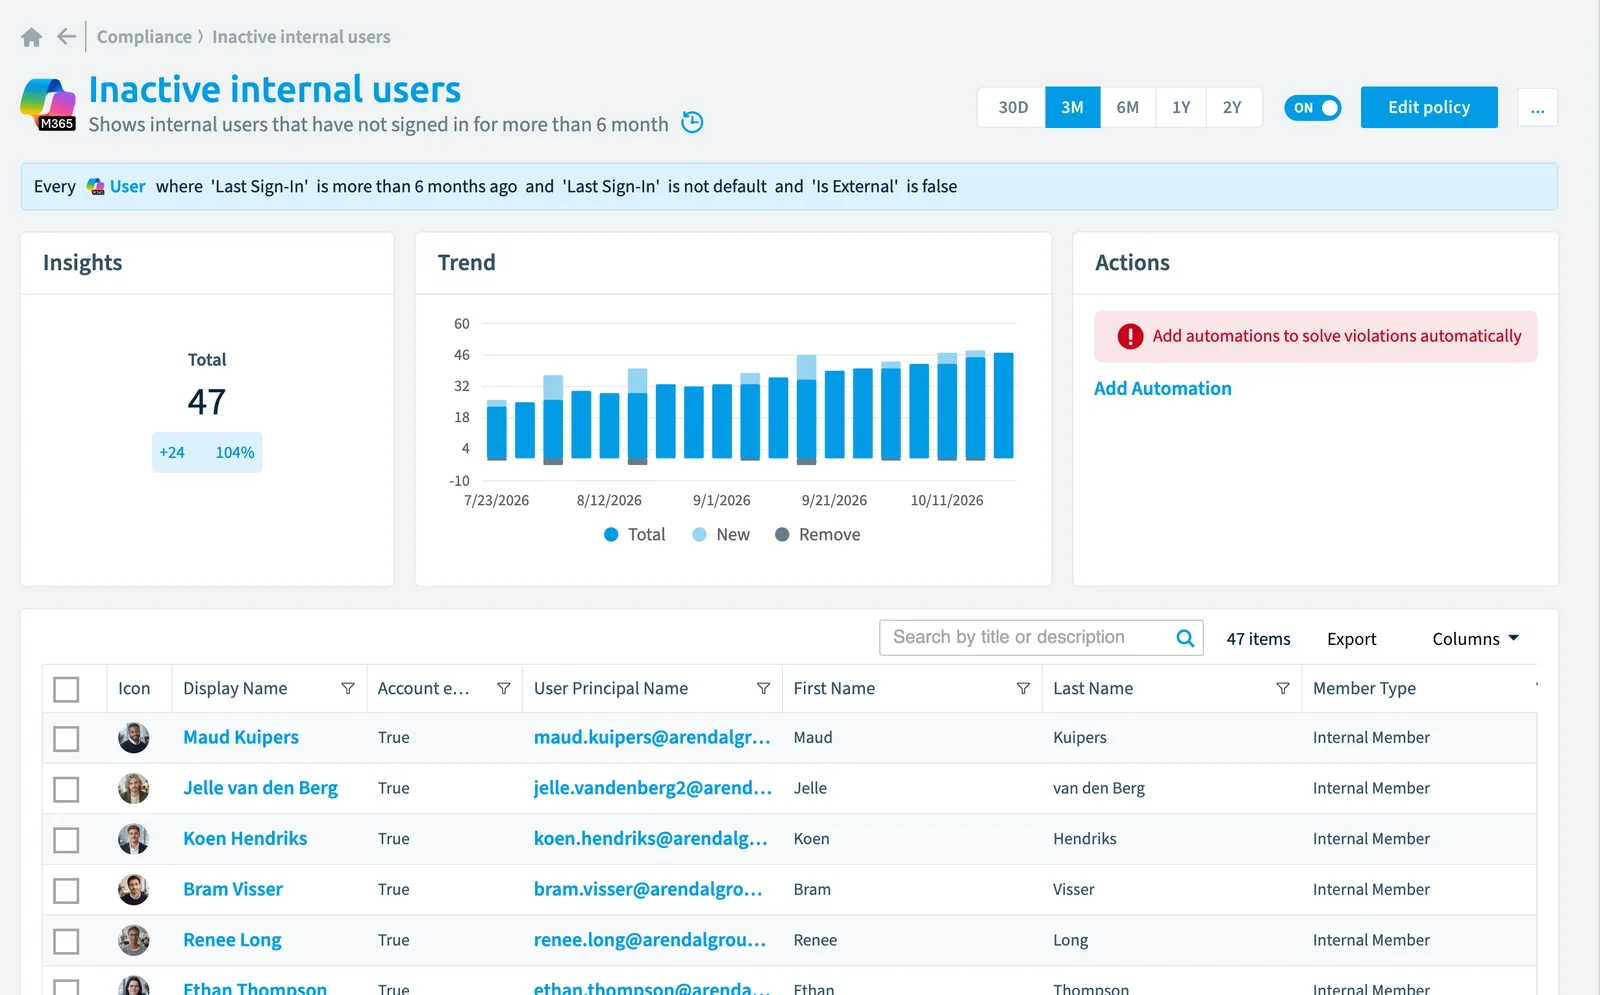
Details
| Applies to | User |
|---|---|
| Connector | Microsoft 365 |
| Severity | Medium |
| Category | External Access |
| Recommended | No |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check User objects:
- Copilot adoption opportunity - E3/E5 users (Medium)
- Copilot license assigned to disabled account (High)
- Inactive Copilot users - 30 days (Medium)
- Excessive draft agent creation pattern (Medium)
- External users (Information)
- External users with pending acceptance (Low)
- Users with Power Platform Premium license (Information)
- Users with E3 license not using Outlook in last 12 month (Low)
- Users with passwords not changed in last 6 months (Medium)
- Disabled user accounts (Medium)
- Admin accounts with an Office 365 E3 license assigned (Medium)
- Administrators without MFA (High)
- External users invited 3 month ago with pending acceptance (Low)
- Disabled user accounts with assigned licenses (High)
- Global administrators without MFA (High)
- Guest users with a Dynamics license assigned (Medium)
- Inactive external users (Medium)
- Over-licensed user accounts (High)
- Users who are creating Microsoft Loop Teams components (Medium)
Frequently asked questions
What does the inactive internal users policy detect?
The Inactive internal users policy shows internal users that have not signed in for more than 6 months.
Which objects does the inactive internal users policy check?
The Inactive internal users policy checks User objects from the Microsoft 365 inventory and reports each one that matches its rule as a violation.
How severe is a violation of the inactive internal users policy?
Violations of the Inactive internal users policy have Medium severity. The policy is in the External Access category.
Which module includes the inactive internal users policy?
The Inactive internal users policy comes with the Microsoft 365 connector in the Digital Workplace module of Rencore Governance, which every Plan includes.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?