ChatGPT login bypassed SSO
AI summary
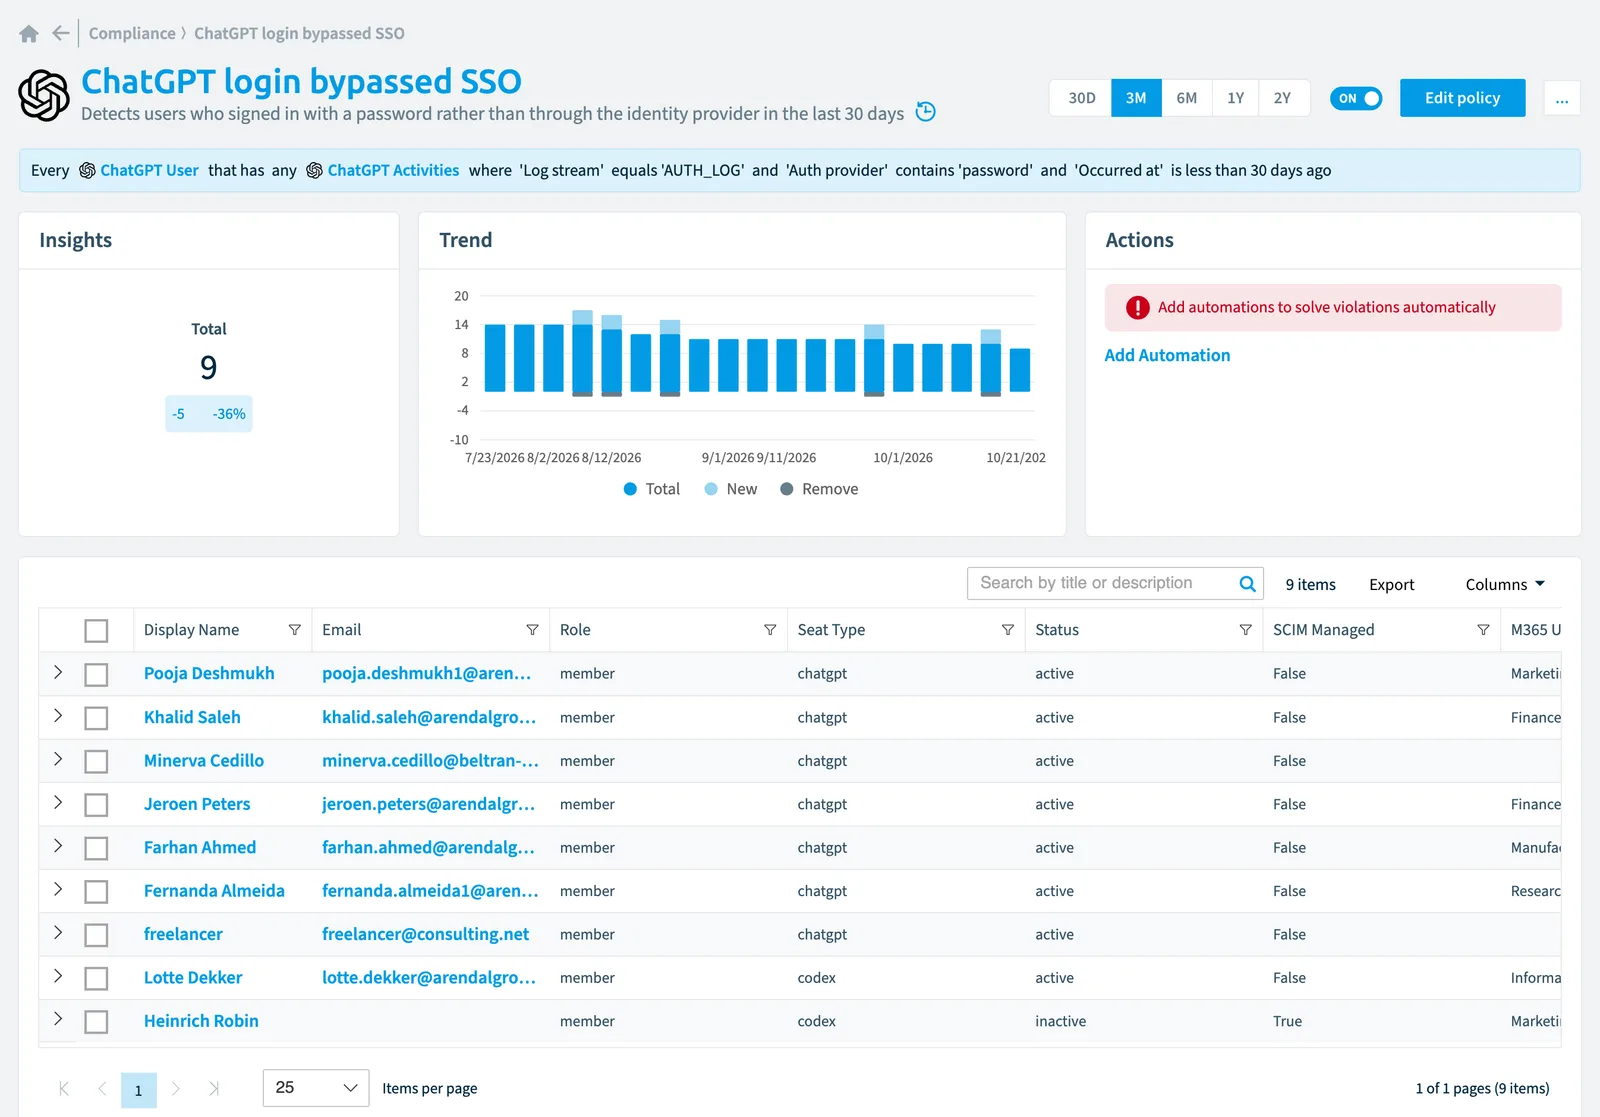
Use this policy to identify ChatGPT users who signed in with a password rather than through your identity provider in the last 30 days. Password logins bypass conditional access, MFA, and session controls; findings indicate configuration gaps or accounts that predate SSO enforcement.
What it detects
Detects users who signed in with a password rather than through the identity provider in the last 30 days.
Why it matters
A password login sidesteps conditional access, MFAMultifactor authenticationMultifactor authentication asks a user for a second form of verification, such as a code on their phone or a fingerprint, in addition to the password.Read more policy and session controls in one step. Where SSO is enforced this should not be possible, so a finding here usually means either a configuration gap or an account that predates enforcement. Login history starts at the connect date, so an empty result on a young connection is not evidence of compliance.
The rule
Every ChatGPT User that has any ChatGPT Activities where Log stream equals 'AUTH_LOG' and Auth provider contains 'password' and Occurred at is less than 30 days ago
In Rencore Governance
Details
| Applies to | ChatGPT user |
|---|---|
| Connector | ChatGPT Enterprise |
| Severity | High |
| Category | Security |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check ChatGPT user objects:
- Codex seat with no Codex usage (Low)
- Idle ChatGPT seat (Low)
- Inactive user still holding objects (High)
- Manually managed ChatGPT user (Medium)
- ChatGPT user with no Entra ID identity (High)
- ChatGPT user with no spend cap (Medium)
- ChatGPT user over 80% of their spend cap (Medium)
Frequently asked questions
What does the ChatGPT login bypassed SSO policy detect?
What does the ChatGPT login bypassed SSO policy detect?The ChatGPT login bypassed SSO policy detects users who signed in with a password rather than through the identity provider in the last 30 days.
Which objects does the ChatGPT login bypassed SSO policy check?
Which objects does the ChatGPT login bypassed SSO policy check?The ChatGPT login bypassed SSO policy checks ChatGPT user objects from the ChatGPT Enterprise inventory and reports each one that matches its rule as a violation.
How severe is a violation of the ChatGPT login bypassed SSO policy?
How severe is a violation of the ChatGPT login bypassed SSO policy?Violations of the ChatGPT login bypassed SSO policy have High severity. The policy is in the Security category.
Which module includes the ChatGPT login bypassed SSO policy?
Which module includes the ChatGPT login bypassed SSO policy?The ChatGPT login bypassed SSO policy comes with the ChatGPT Enterprise connector (in preview) in the AI & Agents module of Rencore Governance, an add-on module on the Premium and Enterprise Plans.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?