Workspace-wide custom GPTs with editable configuration
AI summary
Custom GPTs accessible to your entire workspace with edit permissions can be modified by any team member, including the GPT's instructions and external actions. Rencore Governance detects this configuration so you can fix it by restricting sharing or removing write permission in the GPT's settings.
What it detects
Detects custom GPTsCustom GPTA custom GPT is a version of ChatGPT that someone in your ChatGPT Enterprise workspace configured for one purpose and can share with others.Read more every workspace member can reach and edit.
Why it matters
A GPT shared with the whole workspace and left writable can be changed by anyone, including its instructions and the external actions it calls. That turns a single misconfiguration into a workspace-wide one, and the audit trail only shows who authored the latest version rather than who could have. Narrow the sharing, or remove write permission and keep read, in the GPT's settings: the Admin API cannot change either, and Isolate only removes the people it was shared with by name.
The rule
Every ChatGPT Custom GPT where Workspace Wide is true and Can Write is true
In Rencore Governance
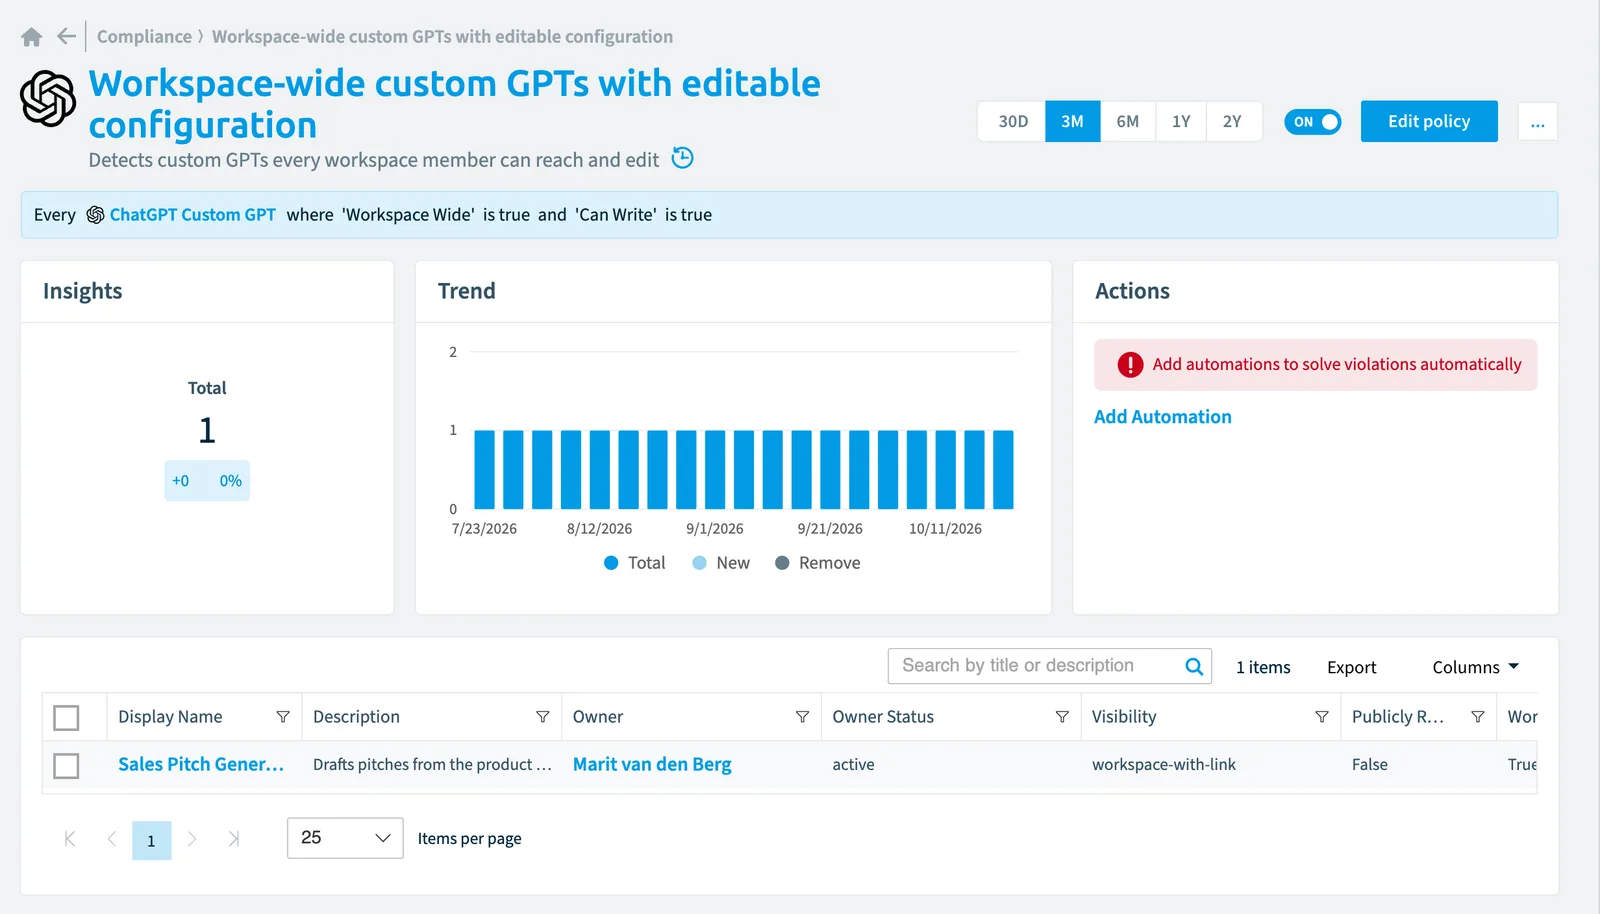
Details
| Applies to | ChatGPT custom GPT |
|---|---|
| Connector | ChatGPT Enterprise |
| Severity | Medium |
| Category | Information Oversharing |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check ChatGPT custom GPT objects:
Frequently asked questions
What does the Workspace-wide custom GPTs with editable configuration policy detect?
The Workspace-wide custom GPTs with editable configuration policy detects custom GPTs every workspace member can reach and edit.
Which objects does the Workspace-wide custom GPTs with editable configuration policy check?
The Workspace-wide custom GPTs with editable configuration policy checks ChatGPT custom GPT objects from the ChatGPT Enterprise inventory and reports each one that matches its rule as a violation.
How severe is a violation of the Workspace-wide custom GPTs with editable configuration policy?
Violations of the Workspace-wide custom GPTs with editable configuration policy have Medium severity. The policy is in the Information Oversharing category.
Which module includes the Workspace-wide custom GPTs with editable configuration policy?
The Workspace-wide custom GPTs with editable configuration policy comes with the ChatGPT Enterprise connector (in preview) in the AI & Agents module of Rencore Governance, an add-on module on the Premium and Enterprise Plans.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?