Shared Codex environment with repository access
AI summary
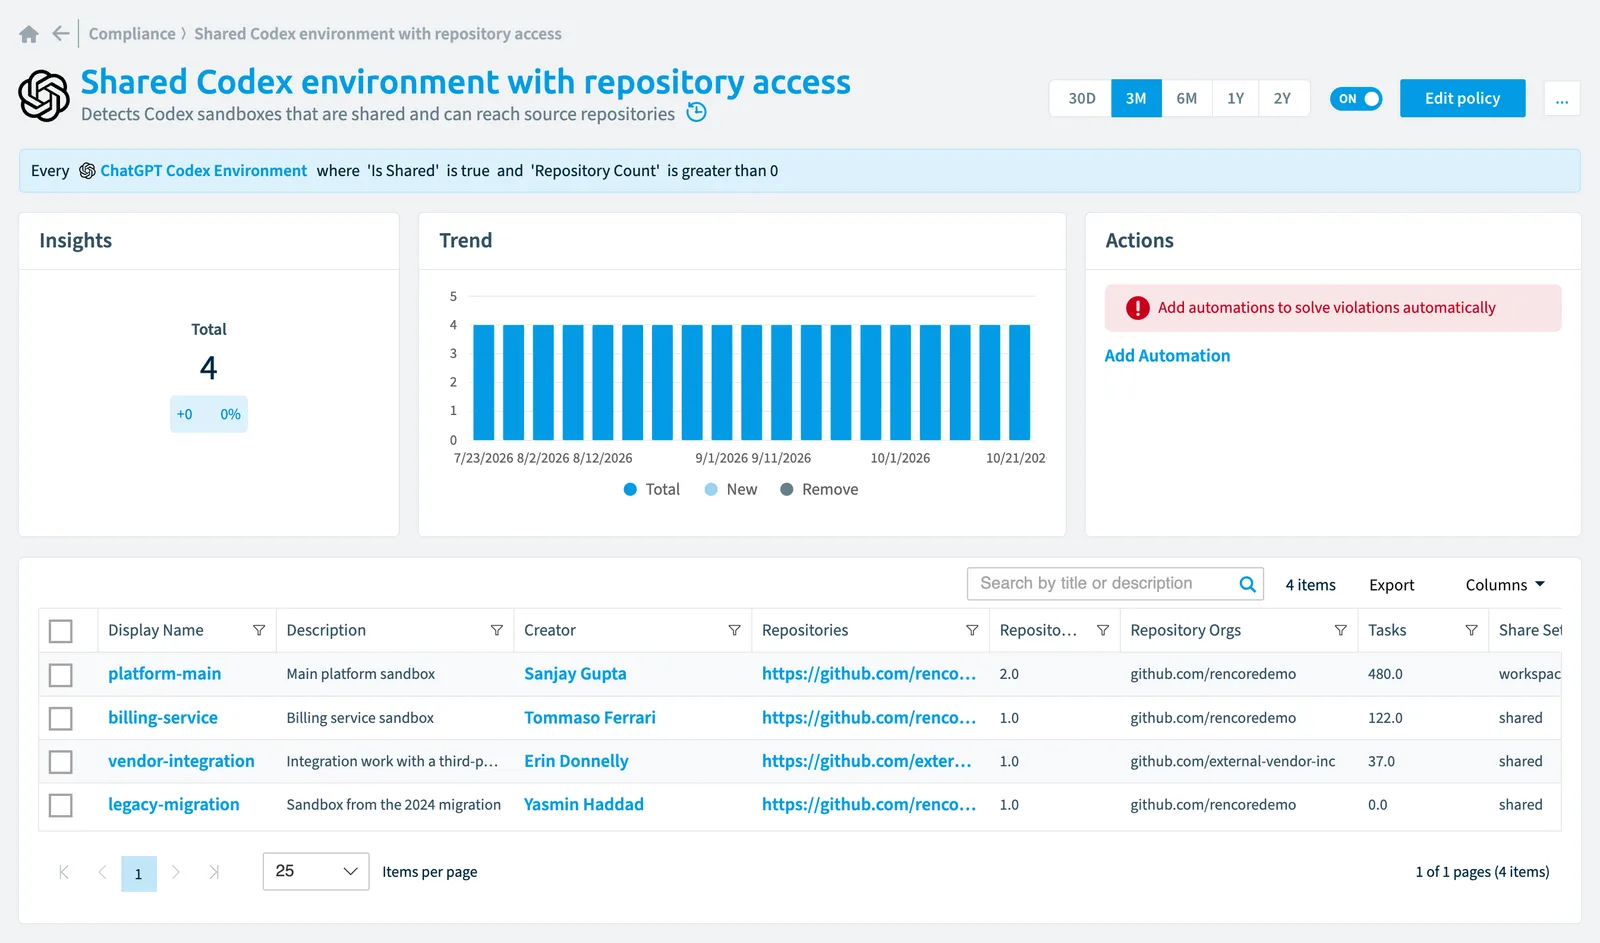
Shared ChatGPT Codex environments with repository access allow all shared users to run code against those repositories, creating a risk of ungoverned data movement. Use this security policy rule to identify and manage such configurations in your deployment.
What it detects
Detects CodexChatGPT CodexCodex is the OpenAI coding agent that is part of a ChatGPT Enterprise workspace.Read more sandboxes that are shared and can reach source repositories.
Why it matters
A shared sandbox grants everyone it is shared with the ability to run code against the repositories it is wired to. Agentic coding is where ungoverned data movement is most likely, and a sandbox outlives the task it was created for. To check the repositories against an approved list, maintain the allowed organisations as a custom propertyCustom MetadataCustom Metadata is a Rencore Governance add-on that adds your own business fields to the inventory, such as cost centers or project codes.Read more and compare them with the Repository Orgs field.
The rule
Every ChatGPT Codex Environment where Is Shared is true and Repository Count is greater than 0
In Rencore Governance
Details
| Applies to | ChatGPT Codex Environment |
|---|---|
| Connector | ChatGPT Enterprise |
| Severity | High |
| Category | External Access |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check ChatGPT Codex Environment objects:
Frequently asked questions
What does the shared Codex environment with repository access policy detect?
The Shared Codex environment with repository access policy detects Codex sandboxes that are shared and can reach source repositories.
Which objects does the shared Codex environment with repository access policy check?
The Shared Codex environment with repository access policy checks ChatGPT Codex Environment objects from the ChatGPT Enterprise inventory and reports each one that matches its rule as a violation.
How severe is a violation of the shared Codex environment with repository access policy?
Violations of the Shared Codex environment with repository access policy have High severity. The policy is in the External Access category.
Which module includes the shared Codex environment with repository access policy?
The Shared Codex environment with repository access policy comes with the ChatGPT Enterprise connector (in preview) in the AI & Agents module of Rencore Governance, an add-on module on the Premium and Enterprise Plans.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?