
SharePoint agent references confidential site without approval
AI summary
SharePoint agents accessing confidential sites without approval risk data leaks through unauthorized AI responses. This security rule in Rencore Governance lets you identify such agents and enforce mandatory review before deployment.
What it detects
Identifies SharePoint agents connected to confidential sites without approval, increasing the risk of unauthorized AI-generated responses.
Why it matters
Unapproved SharePoint agents referencing confidential sites risk data leaks. Organizations should enforce a mandatory approval process via Rencore Governance to review agent connections before deployment. Limit agent permissions to prevent unauthorized data access.
The rule
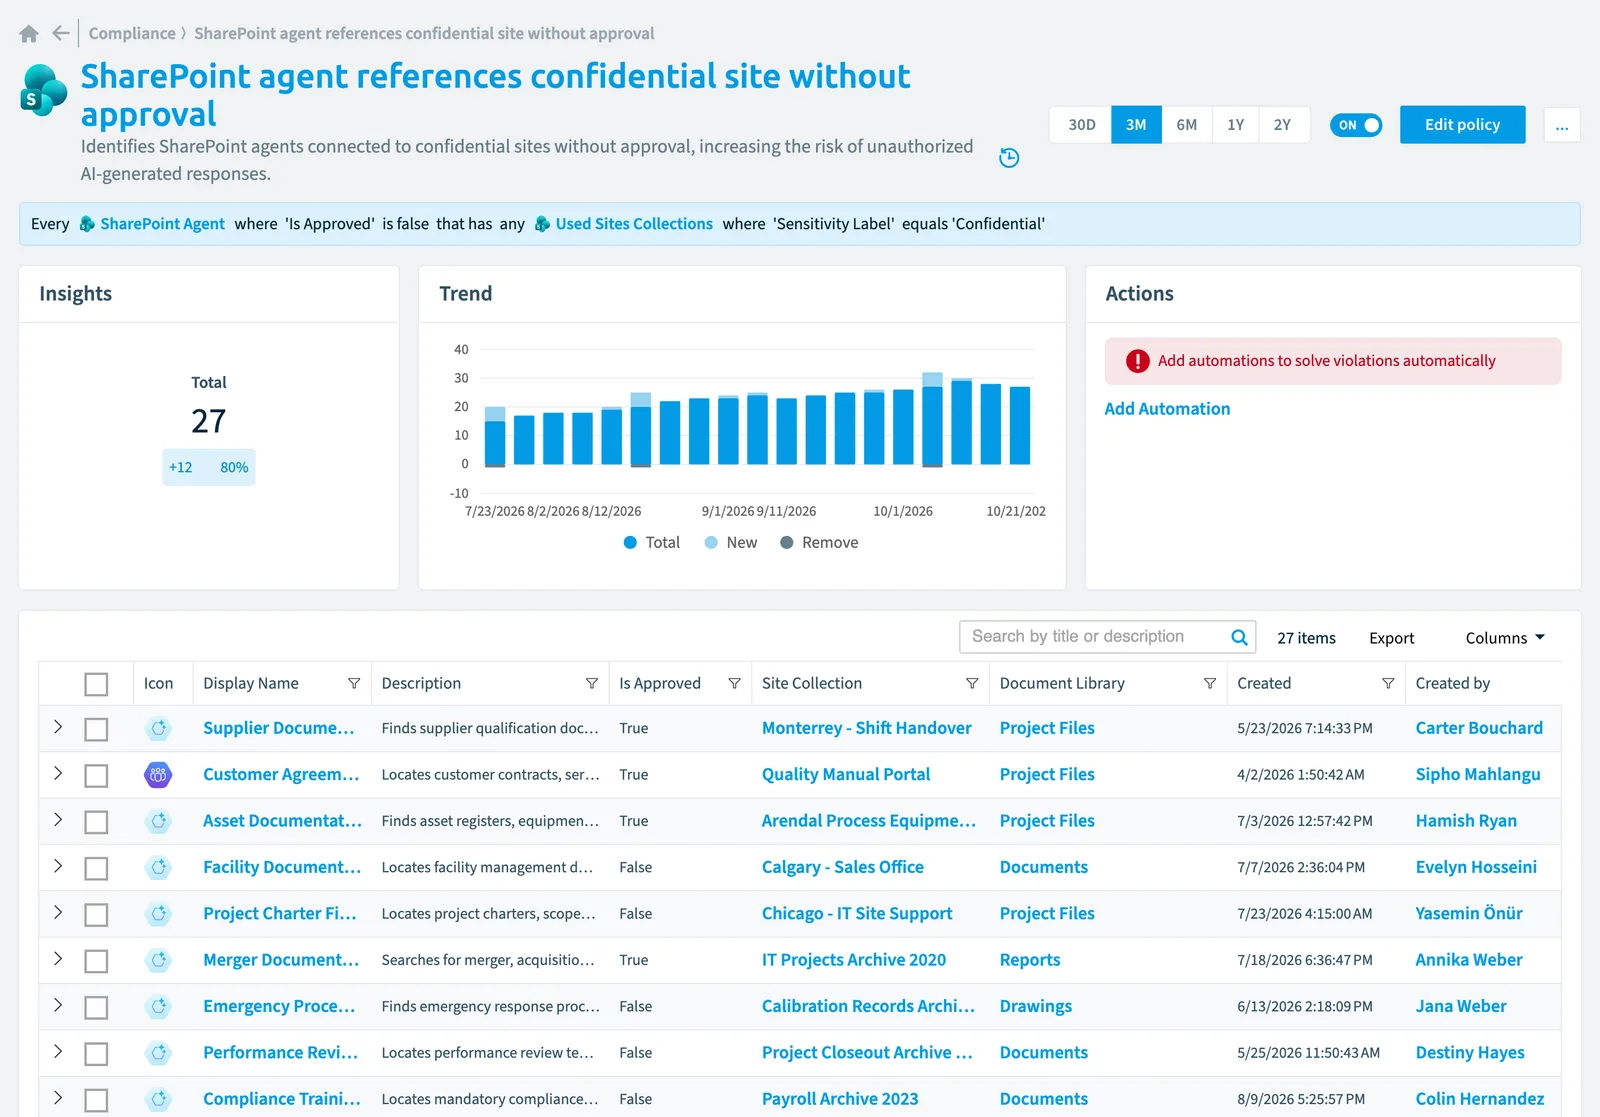
Every SharePoint Agent where Is Approved is false that has any Used Sites Collections where Sensitivity Label equals 'Confidential'
In Rencore Governance
Details
| Applies to | SharePoint agent |
|---|---|
| Connector | SharePoint |
| Severity | High |
| Category | Security |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check SharePoint agent objects:
Frequently asked questions
What does the SharePoint agent references confidential site without approval policy detect?
What does the SharePoint agent references confidential site without approval policy detect?The SharePoint agent references confidential site without approval policy identifies SharePoint agents connected to confidential sites without approval, increasing the risk of unauthorized AI-generated responses.
Which objects does the SharePoint agent references confidential site without approval policy check?
Which objects does the SharePoint agent references confidential site without approval policy check?The SharePoint agent references confidential site without approval policy checks SharePoint agent objects from the SharePoint inventory and reports each one that matches its rule as a violation.
How severe is a violation of the SharePoint agent references confidential site without approval policy?
How severe is a violation of the SharePoint agent references confidential site without approval policy?Violations of the SharePoint agent references confidential site without approval policy have High severity. The policy is in the Security category.
Which module includes the SharePoint agent references confidential site without approval policy?
Which module includes the SharePoint agent references confidential site without approval policy?The SharePoint agent references confidential site without approval policy comes with the SharePoint connector in the Digital Workplace module of Rencore Governance, which every Plan includes.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?