
SharePoint file is shared with external users
AI summary
SharePoint files shared externally can expose sensitive data and create compliance risks. Rencore Governance automatically detects these files and alerts you for review and action.
What it detects
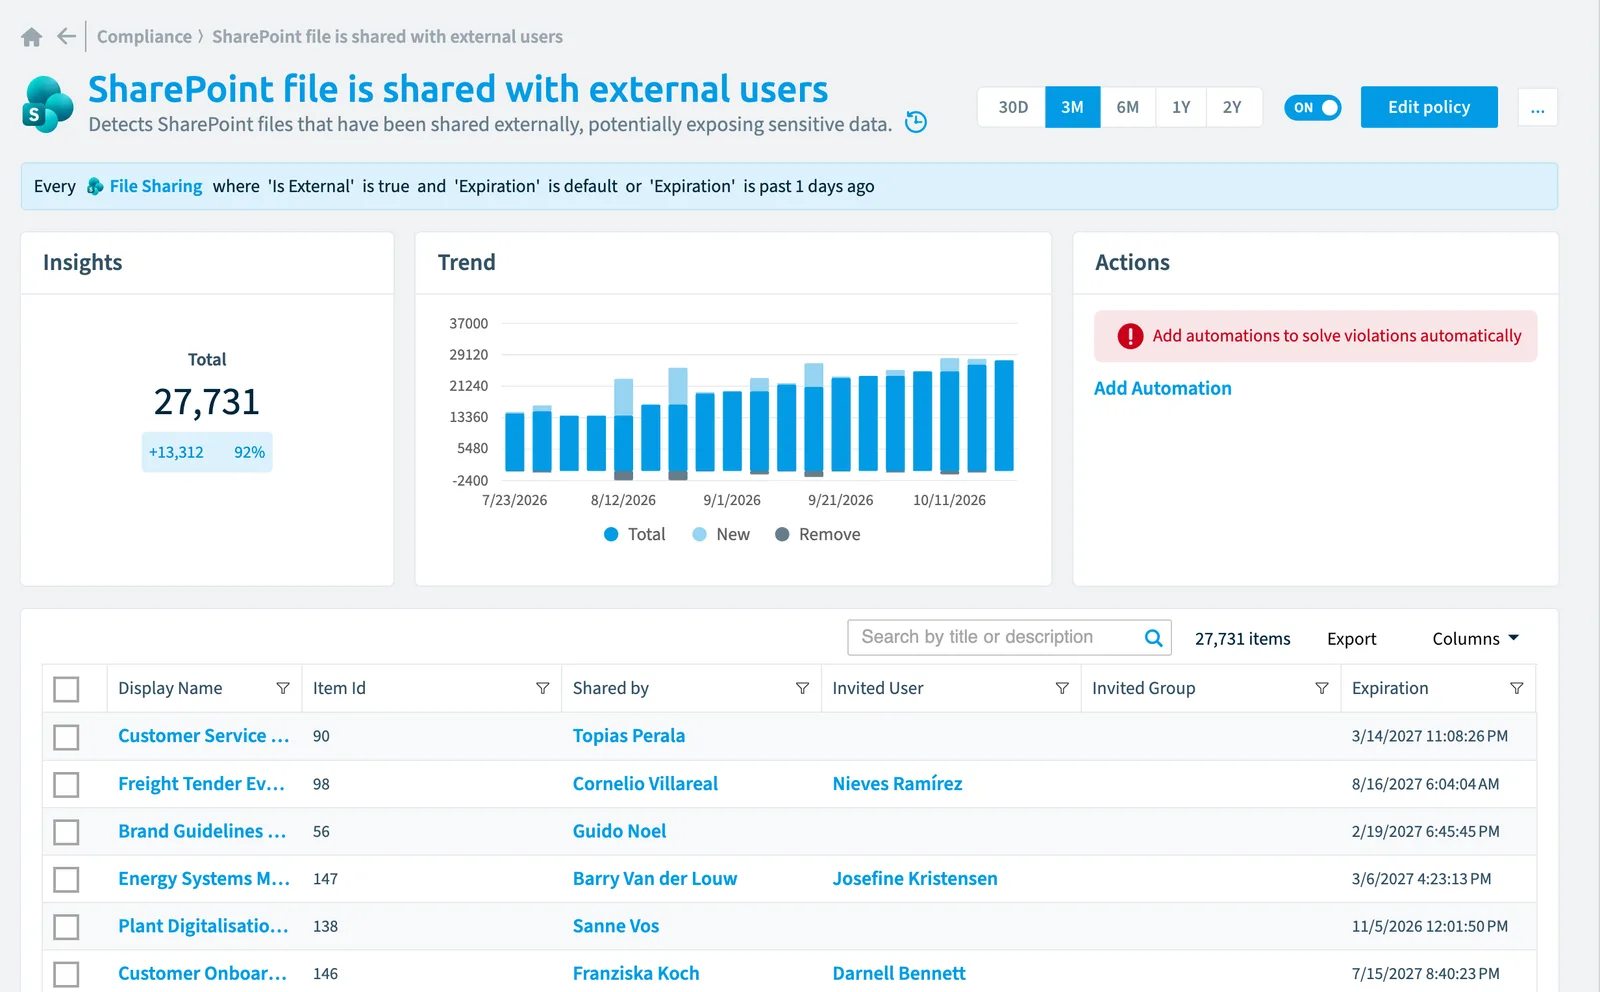
Detects SharePoint files that have been shared externally, potentially exposing sensitive data.
Why it matters
Sharing SharePoint files externally without control can lead to data leaks and compliance risks. Organizations should use Microsoft Purview sensitivity labelsSensitivity labelA sensitivity label is a Microsoft Purview classification, such as Confidential or Internal, that an organization applies to content and to containers such as Teams and SharePoint sites.Read more and enforce Data Loss Prevention (DLP) policies to protect confidential content. Rencore Governance can automate external file sharingSharing linkA sharing link is a link in SharePoint or OneDrive that grants access to a file or folder, sometimes to people outside your organization.Read more detection and notify administrators for review and action. Establish a need-to-share" policy where data is only shared externally when strictly necessary.
The rule
Every File Sharing where Is External is true and Expiration is default or Expiration is past 1 days ago
In Rencore Governance
Details
| Applies to | File sharing |
|---|---|
| Connector | SharePoint |
| Severity | High |
| Category | Security |
| Recommended | Yes |
| Recommended automation | None |
| License type | Standard |
Related policies
Other policies that check File sharing objects:
Frequently asked questions
What does the SharePoint file is shared with external users policy detect?
What does the SharePoint file is shared with external users policy detect?The SharePoint file is shared with external users policy detects SharePoint files that have been shared externally, potentially exposing sensitive data.
Which objects does the SharePoint file is shared with external users policy check?
Which objects does the SharePoint file is shared with external users policy check?The SharePoint file is shared with external users policy checks File sharing objects from the SharePoint inventory and reports each one that matches its rule as a violation.
How severe is a violation of the SharePoint file is shared with external users policy?
How severe is a violation of the SharePoint file is shared with external users policy?Violations of the SharePoint file is shared with external users policy have High severity. The policy is in the Security category.
Which module includes the SharePoint file is shared with external users policy?
Which module includes the SharePoint file is shared with external users policy?The SharePoint file is shared with external users policy comes with the SharePoint connector in the Digital Workplace module of Rencore Governance, which every Plan includes.
Was this page helpful?
Thanks for the feedback.
Thanks. What was wrong?